Supplier Security Symposium 2026
One day. The sharpest minds in automotive cybersecurity. Built for the supply chain.
1 Day
Intensive
300+
Attendees
20+
Speakers
Free
to Attend
Organized by


Why Attend?
-
A Response to Rising Expectations
Increasing interconnectivity and growing demands from customers and partners are putting new pressure on automotive suppliers. This event helps you understand what's changing, and what it means for your organization.
-
Customer Requirements & TISAX in Focus
Get concrete orientation on what OEMs actually expect from their supply chain, how TISAX-related practices apply in reality, and what the business impact of capable versus insufficient supplier security looks like.
-
Real-World Lessons, Not Just Theory
Sessions draw on applied approaches and honest accounts of open challenges, bringing practitioner-level insights from people navigating the same pressures you face.
-
Built for Suppliers of All Sizes
Designed for decision-makers, security experts, and operational practitioners at suppliers in the Detroit Metro area, including small and mid-sized enterprises often underserved by larger industry events.
-
Strategic Depth & Hands-On Exchange
Plenary sessions set the strategic context; interactive workshops let you go deeper. The format is content-driven and practice-oriented, built for exchange, not promotion.
Event Details
- Date
- Wednesday, October 28, 2026
- Time
- 8:00 AM – 6:00 PM (Eastern Time). Registration and breakfast from 7:00 AM
- City
- Novi, Michigan, USA
- Format
- In-person, full-day conference
- Language
- English
- Cost
- Complimentary for qualified attendees
Agenda
October 28, 2026 · 8:00 AM – 6:00 PM · Vibe Credit Union Showplace, Novi, MI
Moderation: (ENX Association)
-
Registration & Coffee
-
The Front Line Has Vanished: Welcome & Opening Remarks
-
(ENX Association, Managing Director)
-
-
The Cyber Threat Landscape: What We Are Seeing and Why It Matters
The FBI's view of today's cybercrime landscape: which threats are causing real-world damage, why organizations of every size are targeted, and how a cyber incident quickly becomes a business incident.
-
(FBI, Leader, Detroit Cyber Task Force)
-
-
Our Security Depends on You: Strengthen the LINK, Protect What Moves Us
An automaker's perspective on why supplier resilience is OEM resilience: how supplier incidents ripple through production, and what a common security baseline and industry-wide collaboration can do about it.
-
(Stellantis, Cybersecurity Business Partner Lead)
-
-
Panel: From Incidents to Action: Scaling up Security throughout the Industry
Security leaders from across the industry discuss what is already working, what needs to happen next, and how to focus limited resources where they matter most, both inside each organization and across thousands of suppliers.
-
(Stellantis, Cybersecurity Business Partner Lead)
-
(BMW, Principal CSO Strategy and Governance, Information Security)
-
(FBI, Leader, Detroit Cyber Task Force)
-
(Yazaki NA, Head of Information Technology)
-
-
Coffee Break & Networking
Refreshments and partner exhibit time.
-
TISAX, Trust, And Resilience: Securing the Automotive Supply Chain
Industry leaders share lessons learned on meeting OEM cybersecurity expectations, managing customer and regulatory requirements, and scaling security across global operations, and on how TISAX, third-party risk management, and collaboration strengthen the whole ecosystem.
-
(Inteva, Director Cyber & Information Security)
-
(Yazaki, Head of Cybersecurity YNCA and EMEA)
-
(BorgWarner, CISO), Moderation
-
(Bosch, Mobility Security)
-
(Joyson, CISO)
-
-
Lunch & Networking
Dedicated time for informal discussion, booth visits, and building connections across organizations.
-
Keynote: What I Wish Every Supplier Would Do Tomorrow
An interactive session on practical lessons from managing cyber risk across a complex automotive ecosystem, including a walk through a realistic incident and how business and security leaders respond to it.
-
(Stellantis, Regional CISO North America)
-
-
Case Study: Practical Changes for a Positive Impact
A grounded look at security improvement in small and mid-sized enterprises, covering physical security, a management perspective, and open Q&A, illustrated through real-world experience at the Marelli Southfield site.
-
(Marelli, Global CISO)
-
Mat Hall (Marelli)
-
-
Coffee Break & Networking
Refreshments and open networking.
-
From Examples to Confidence: A Common Toolset for Security, Resilience, and Trust
How TISAX and industry collaboration form part of the solution for securing the automotive supply chain.
-
(ENX Association, Head of ACARS and R&D)
-
-
Building Resilience: We Don't Have to Do it Alone
Cybersecurity can feel overwhelming, especially for smaller companies. Resilience is achievable step by step, and the industry has a major advantage: no one has to figure it out alone.
-
(Marelli, Global CISO)
-
-
Closing Remarks
Final words from ENX leadership to wrap up the day.
-
(ENX Association, Managing Director)
-
-
Reception & Networking, Individual Q&A
Food, drinks, and open networking, with potential giveaways and partner raffles.
-
End of Symposium
Thank you for joining us. Safe travels.
Meet ENX Association
The ENX team is on site throughout the day. Stop by to ask questions, talk TISAX, and share your feedback with us.
Lennart Oly
Managing Director
ENX Association
Also speaking
Andrew Sczygielski
Leader, Detroit Cyber Task Force
FBI
Eric Fishtahler
Cybersecurity Business Partner Lead
Stellantis
Eric Fishtahler, CISSP, CISA, is Director, Cybersecurity Business Partner at Stellantis, where he leads efforts to integrate cybersecurity into business priorities and strengthen cyber resilience across Stellantis and its extended ecosystem.
His responsibilities include advancing third-party cyber risk management across suppliers, affiliates and joint ventures, with a focus on building stronger relationships, improving resilience and making cyber risk practical and actionable.
Eric brings extensive experience across cybersecurity, technology risk and internal audit. Before joining the CISO organization, he led technology audit at Stellantis, following earlier leadership roles at Kelly Services and Deloitte. He holds a B.A. from Michigan State University.
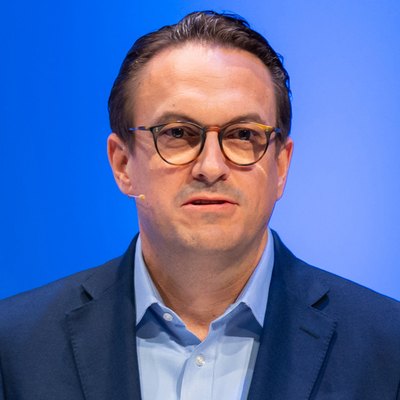
Sven Hirschke
Principal CSO Strategy and Governance, Information Security
BMW
Sven Hirschke is Vice President and Board Member of the ENX Association and a senior security and digital transformation executive at BMW Group, with more than 20 years of international leadership experience.
He established and led BMW Group's global Information Security function, pioneering an integrated security governance approach spanning IT, secrecy, connected products, manufacturing and global supply chains. As a co-initiator of TISAX, he has helped advance global information security standards and trusted collaboration across the automotive ecosystem.
His expertise spans corporate and information security, supply chain resilience, enterprise risk management, and AI and digital transformation, with a strong focus on security and trust across interconnected industrial ecosystems.
Also speaking
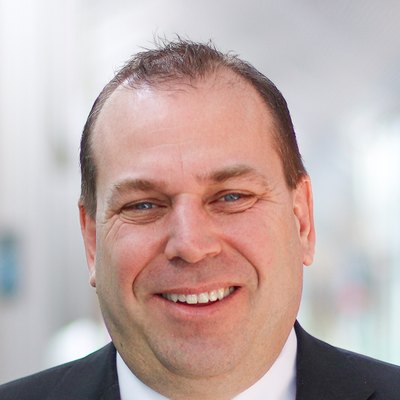
Ryan Spencer
Head of Information Technology
Yazaki NA
Ryan Spencer is Vice President of Information Technology for Yazaki North America and Yazaki Europe Middle East Africa, part of the Yazaki Group, one of the world's largest privately owned automotive suppliers. He leads technology strategy, implementation and support for Yazaki's North and Central American operations and all of its European operations.
Ryan focuses on cross-functional collaboration and on using best practices and technology to drive efficiency across the organization. Before joining Yazaki eight years ago, he spent two years with Dura Automotive and 26 years with Takata, where he was Vice President of Information Technology.
He holds an MBA from the University of Michigan and a bachelor's degree in Electrical Engineering from Kettering University (formerly GMI). He teaches IT strategy as an adjunct professor in Oakland University's Executive MBA program and serves on several university advisory boards in Michigan.
Also speaking
Ahmeed Ahmeed
Director Cyber & Information Security
Inteva
Also speaking
Janette Barretto
Head of Cybersecurity YNCA and EMEA
Yazaki
Also speaking
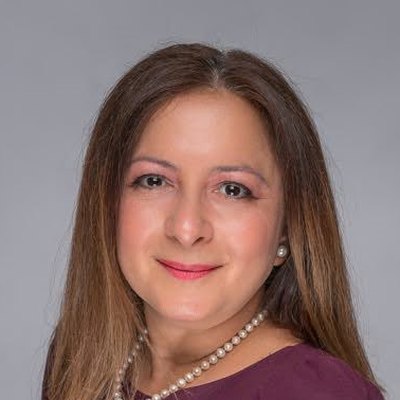
Juman Doleh-Alomary
CISO
BorgWarner
Juman Doleh-Alomary is the Global Chief Information Security Officer at BorgWarner, based in Auburn Hills, Michigan, with more than 15 years of experience in cybersecurity, risk management, compliance and privacy. She leads a globally distributed team that shapes and executes the company's cybersecurity strategy, including IT and OT security, third-party risk management, and regulatory initiatives such as TISAX, NIS2 and the EU Cyber Resilience Act.
Before BorgWarner, she was Director of Cybersecurity Governance, Risk & Compliance at Little Caesars and held leadership roles at Wayne State University and Ford Motor Company. Juman partners closely with executive leadership and the board on security governance and business alignment, and is an active leader in the cybersecurity community, supporting organizations that advance women in technology and cybersecurity.
Also speaking
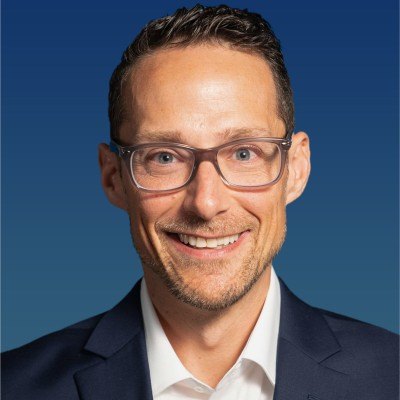
Anthony Freilach
Mobility Security
Bosch
Also speaking
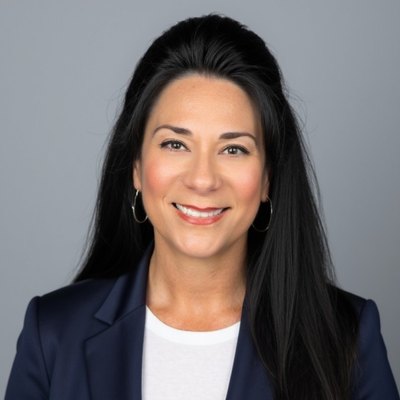
Maria Haight
CISO
Joyson
Also speaking
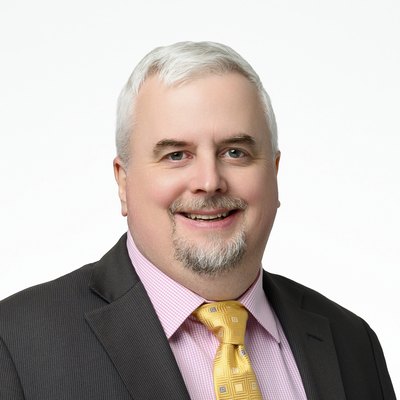
Matthew Schie
Regional CISO North America
Stellantis
Matthew Schie is the Regional Information Security Officer for Stellantis North America. He has spent his career in cybersecurity, beginning at Symantec and going on to hold leadership roles in security architecture, privacy, IT risk and global incident response.
About a decade ago, together with colleagues at other OEMs, he helped create, and was a signatory of, the first North American Automotive Industry Third-Party Information Security Requirements standard, establishing common cybersecurity expectations for suppliers and business partners across the automotive ecosystem.
Outside work, Matthew is a veteran, an astronomy outreach educator and an elected official.
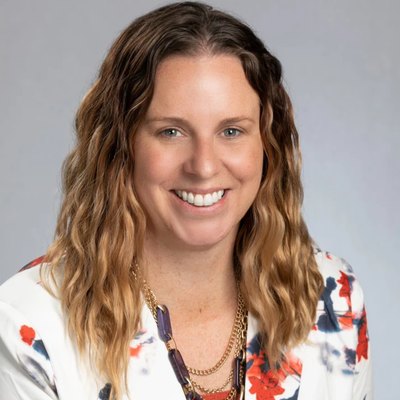
Kristie Pfosi
Global CISO
Marelli
Also speaking
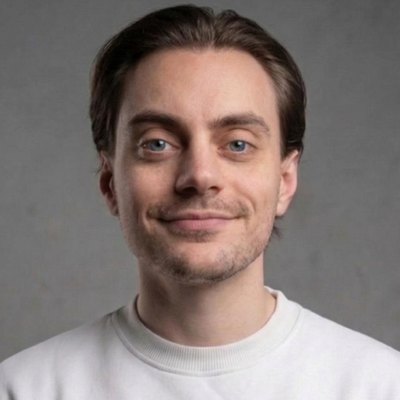
Jean Daninos
Security Engineer
ENX Association
Jean Daninos has been a Security Engineer at the ENX Association for around three years, looking after the ENX Network, working on TISAX-related topics and contributing to the association's global development.
Also speaking
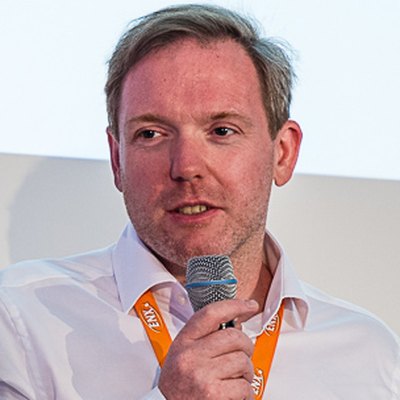
Immo Wehrenberg
Head of ACARS and R&D
ENX Association
Also speaking
Our Partners
Auto-3S 2026 is made possible by the support of our partners.






Become a Partner
Showcase your brand to 300+ automotive cybersecurity professionals. Limited partnership packages available.
Inquire About Partnership